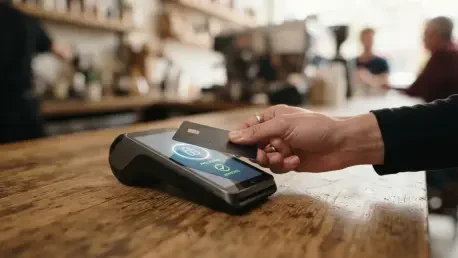
Point of Sale malware allows cybercriminals to harvest credit card data directly from the hardware that serves as the lifeblood of retail and restaurant operations. This specialized threat is merely the tip of a much larger iceberg in a business environment where digital integration has become mandatory for survival. While these technological advancements have enabled small enterprises to compete on a global stage and streamline their daily functions, they have also created a dense landscape of vulnerability that many owners are only beginning to comprehend. The modern economy demands constant connectivity, yet this very link serves as a potential gateway for malicious actors who operate with increasing sophistication and frequency. As small firms transition their essential operations to cloud-based systems and digital payment processors, the perimeter they must defend has expanded far beyond the physical walls of their offices. This shift requires a fundamental reassessment of what it means to be a secure business, moving away from simple locks and alarms toward a comprehensive strategy of digital resilience. The reality is that no enterprise is too small to be noticed by those looking to exploit a weak point in the digital chain.
The Alarming Scale: Analyzing Modern Digital Threats
Recent data suggests that the threat to small businesses is reaching a breaking point, with a vast majority of firms reporting security incidents in the current operational cycle. Approximately 81% of small businesses experienced a security or data breach within a single year, highlighting a relentless pace of criminal activity that shows no signs of slowing. This frequency directly contradicts the common “fly under the radar” mentality that many entrepreneurs adopt when prioritizing their administrative expenses. Many owners assume that their relatively low public profile makes them invisible to international hacking syndicates, but automated scanning tools do not discriminate based on brand recognition. Instead, these tools seek out specific vulnerabilities in software and network configurations, hitting targets of opportunity regardless of their size or industry. This persistent environmental risk means that a breach is no longer a matter of if, but a matter of when for the average local enterprise.
The financial fallout from these incidents is rarely minor and often proves terminal for the business involved if adequate protections are not in place. Statistics from current industry reports show that over 60% of small businesses suffering a breach incur losses exceeding $250,000, a sum that can easily wipe out annual profits or exhaust liquid capital. These costs are not limited to the immediate theft of funds but include the expensive process of forensic investigation, hardware replacement, and potential legal fees. Despite these staggering stakes, a significant preparedness gap exists across the market, with nearly a third of business owners admitting they are entirely unequipped to handle a cyber risk. This lack of readiness often stems from a misunderstanding of the total cost of a breach, which includes long-term brand damage and the loss of customer trust that can take years to rebuild. Without a proactive plan, the immediate cash flow disruption caused by a digital attack can force a permanent closure within months of the initial incident.
The Vulnerability Myth: Why Small Businesses Are Targets
A recurring sentiment among entrepreneurs is that cybercriminals only pursue high-profile corporations with massive treasure troves of data. However, professional hackers are often looking for the easiest entry point rather than the largest prize, functioning much like opportunistic burglars checking for unlocked doors in a neighborhood. Small businesses frequently lack dedicated IT departments and sophisticated security protocols, making them vulnerable to relatively simple exploitation tactics that a larger firm would easily deflect. In many cases, a small business serves as a testing ground for new malware or as a stepping stone to reach a larger partner in the supply chain. The relative ease with which a criminal can infiltrate a small network provides a high return on investment for their time, especially when they can automate attacks against thousands of similar targets simultaneously. This shift in criminal strategy has turned the perceived safety of being “small” into a dangerous liability.
A single compromised login or an unpatched piece of software can grant a criminal unauthorized access to sensitive client files and financial data with minimal effort. Once inside, these actors can execute fraudulent schemes, such as altering payroll information or diverting incoming invoice payments, with little fear of immediate detection. In this context, the lack of robust digital defenses acts as an open invitation to opportunistic hackers looking for a quick payout through low-risk maneuvers. Many small firms use legacy software that no longer receives security updates, or they fail to implement basic network segmentation, allowing a breach in one area to compromise the entire organization. This structural weakness is well-known in the criminal community, where lists of vulnerable small business servers are traded on underground forums. By failing to modernize their digital defenses, business owners are effectively leaving the keys in the ignition of their most valuable assets, hoping that no one notices the opportunity.
High-Risk Sectors: Identifying Industry Specific Vulnerabilities
While any business with an internet connection is at risk, professional and management consultants are particularly exposed due to their role as information brokers. These professionals store strategy documents, intellectual property, and proprietary client data that can serve as keys to larger corporate networks or provide leverage for corporate espionage. Because consultants often have privileged access to their clients’ internal systems, they become high-value targets for those looking to bypass the heavy security of a major corporation. Business Email Compromise remains a primary threat in this sector, often leading to millions of dollars in diverted funds and harvested data through highly targeted phishing campaigns. A consultant’s reputation is their most valuable asset, and a single breach can result in the immediate termination of contracts and a permanent blacklisting within their professional community, making the stakes of digital security an existential concern for their practice.
Financial professionals, such as accountants and advisors, handle what is considered the “gold standard” of stolen data, including Social Security numbers, tax identifiers, and detailed banking information. A breach in this sector triggers a cascade of expensive requirements, such as mandatory client notifications and stringent regulatory penalties imposed by state and federal authorities. The legal framework surrounding financial data privacy is increasingly rigorous, and small firms are held to the same compliance standards as multi-national banks. Cyber liability insurance is specifically designed to manage these post-event expenses that would otherwise fall directly on the firm’s bottom line, covering everything from credit monitoring for victims to the cost of legal representation during government audits. For an independent accountant, the sheer volume of sensitive data managed on a single laptop makes them a concentrated target for ransomware, where the inability to access client files during tax season can lead to a total operational collapse.
Transactional Security: The Crisis of Wire Fraud
Real estate agents and brokers face a unique crisis due to the high-value transactions they manage on a daily basis, involving the transfer of life savings and significant corporate capital. The frequent use of wire transfers creates a high-stakes target for criminals who use sophisticated “spoofing” techniques to impersonate trusted partners, such as title companies or attorneys. By intercepting communication threads and providing fraudulent wiring instructions at the last moment, hackers cause hundreds of millions of dollars in losses annually within the real estate industry. These attacks are often timed to occur on Friday afternoons when banking delays can give the criminals a head start to move the funds through multiple international accounts. For a small real estate firm, the liability associated with a diverted down payment can lead to massive lawsuits and the loss of their professional license, as the responsibility for secure communication often rests with the broker of record.
Creative services and marketing agencies often serve as gateways to their clients’ larger digital assets, making them a strategic target for multi-stage cyberattacks. Because these agencies hold administrative login credentials for various websites, advertising accounts, and social media platforms, they are frequently targeted through social engineering tactics that exploit the collaborative nature of their work. Even sophisticated teams can fall victim to malicious links disguised as routine business invitations or file-sharing notifications, highlighting the need for constant vigilance across every level of the organization. Once an agency’s credentials are stolen, a hacker can launch massive fraudulent ad campaigns or deface a client’s website, causing immediate financial and reputational harm to the client. This interconnected risk means that an agency’s security posture is a critical component of their value proposition, as clients increasingly demand proof of robust digital protections before signing long-term service agreements.
Operational Continuity: Retail Challenges and Malware
For brick-and-mortar businesses, the Point of Sale system represents the lifeblood of the operation and a primary target for sophisticated malware designed to intercept unencrypted data. Cybercriminals use specialized software to harvest credit card information directly from payment terminals during the brief moment when the transaction is being processed. Furthermore, ransomware has become one of the most prevalent threats facing local shops and restaurants, as it locks a business out of its own digital tools until an exorbitant fee is paid. For a small retail store, the inability to process payments for even a single day can result in a terminal cash flow problem, especially during peak shopping seasons. The complexity of modern POS systems, which often integrate inventory management and customer loyalty programs, means that a single point of failure can paralyze every department of the business simultaneously, leaving the owner with no way to track sales or manage staff.
Understanding the tactics used by “black-hat” actors is essential for building a proper defense that goes beyond simple software installation. These tactics range from psychological manipulation in social engineering, where an employee is tricked into revealing a password, to technical exploits like credential theft and automated account takeovers. When a payment channel is lost or sensitive data is encrypted, the resulting pressure to pay a ransom can lead business owners to make desperate decisions that may not even result in the recovery of their data. Criminal groups often target businesses they believe are more likely to pay quickly to avoid public embarrassment or operational downtime. This environment requires a shift in perspective, where cybersecurity is seen not just as a technical hurdle but as a fundamental component of business continuity planning. Without a strategy to handle an immediate digital shutdown, a small shop or restaurant remains highly vulnerable to the predatory practices of global criminal networks.
Defense Strategies: Building a Framework for Resilience
Relying on insurance alone is an incomplete strategy that leaves a business vulnerable to the initial shock of an attack; instead, owners must implement a “defense-in-depth” approach. One of the most effective deterrents available today is the implementation of Multi-Factor Authentication across all business accounts, from email to banking and cloud storage. By requiring a second verification step, such as a code generated on a mobile device or a biometric scan, a business can prevent unauthorized access even if a password has been compromised. This simple addition creates a significant barrier for automated attacks, which often rely on stolen credential lists to gain entry. While it may add a few seconds to the login process, the protection it provides far outweighs the minor inconvenience, effectively neutralizing the threat of most common credential-harvesting schemes. Small business owners should make this a mandatory requirement for every employee who accesses the company network.
Secure payment protocols are equally vital, ensuring that as little customer data as possible is stored on physical hardware located at the business premises. By utilizing tokenization and encrypted payment gateways, businesses can significantly reduce their liability in the event of a system breach, as the data stolen would be useless to the hackers. Furthermore, in an era of deepfakes and sophisticated email fraud, the rule of “trust but verify” must be strictly enforced within the corporate culture. Large wire transfers or urgent requests for funds should always be confirmed via a direct phone call to a known, trusted number rather than relying solely on email communication, which can be easily intercepted or faked. Establishing a clear, written protocol for financial transactions ensures that employees have a standard to follow when they encounter a suspicious or “urgent” request from a supposed executive. These procedural safeguards are often as important as the technical ones in preventing high-value financial theft.
Cultural Security: The Human Element and Insurance
The human element remains the weakest link in any security chain, as a single lapse in judgment or a moment of distraction can compromise an entire enterprise regardless of the software in place. Providing regular, engaging training for employees on how to spot “red flags,” such as misspelled domain names, unusual sender addresses, or requests for secrecy, is a critical investment for any modern firm. This training should not be a dry, one-time lecture but an ongoing conversation that keeps security at the forefront of every team member’s mind. When employees feel empowered to report suspicious activity without fear of being penalized for a mistake, the business gains a human firewall that is far more adaptable than any static security program. Cybersecurity must be treated as a permanent and evolving business function, integrated into the daily workflow rather than relegated to a forgotten checklist item in the employee handbook.
When preventative measures fail despite a company’s best efforts, cyber liability insurance serves as the ultimate financial safety net that prevents a crisis from becoming a catastrophe. These policies typically cover data restoration, allowing firms to hire forensic experts to recover encrypted files or rebuild databases that were deleted during an attack. They also provide essential legal and regulatory support, covering the high costs of defense fees and government penalties that arise following a major data breach involving sensitive information. Beyond the financial payout, many insurance providers offer access to a “breach response team” of experts who can guide a business owner through the complex steps of managing an incident in real-time. This access to specialized knowledge is often the difference between a managed recovery and a chaotic collapse, providing the technical and legal guidance necessary to navigate the immediate aftermath of a digital intrusion.
Future Planning: Ensuring Long-Term Business Survival
The final pillar of a comprehensive security strategy involved the integration of business interruption coverage and the management of notification costs. This specific type of insurance compensated for lost revenue during the time systems remained offline, ensuring that the business could meet its payroll and rent obligations while recovering from an attack. It also managed the legal obligation to notify every affected customer, a process that involved significant postage, printing, and the provision of credit monitoring services which would have otherwise drained the company’s remaining cash reserves. By combining operational security with these financial protections, small businesses successfully insured their survival even after sophisticated attacks threatened their existence. Those who viewed security as an investment in resilience rather than an unnecessary cost were the ones who maintained their market position and customer loyalty through the challenges of the last year.
Business owners moved forward by regularly auditing their security posture, evaluating who had access to critical systems and identifying exactly what sensitive data was stored on their servers. Understanding the immediate impact of a communications or payment shutdown became the first step toward building a truly resilient organization. Protecting a modern business proved to be about more than just locking the front door; it required securing the digital gateway through which the entire modern economy flowed. As the landscape continues to evolve from 2026 to 2028, the commitment to digital hygiene and robust insurance coverage will remain the defining characteristics of successful small enterprises. Leaders who recognized these trends early and took decisive action were able to safeguard the revenue streams they worked so hard to build, ensuring that their legacy remained protected against the ever-changing tactics of the digital underworld. This proactive stance allowed the small business community to thrive in a high-risk environment through the application of technical foresight and strategic risk management.