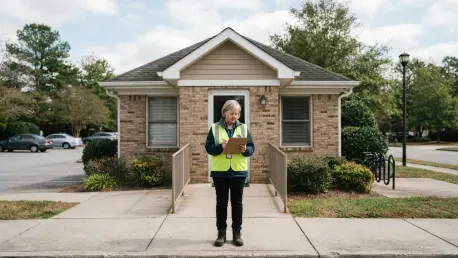
To ensure the accuracy of the CMS database, the government intends to expand its authority to revoke provider enrollments if physical business locations cannot be verified during inspections. This directive sits at the heart of the Comprehensive Regulations to Uncover Suspicious Healthcare, or CRUSH, a sweeping regulatory proposal introduced by the Centers for Medicare & Medicaid Services in late 2026. The framework marks a definitive departure from the historical pay-and-chase methodology that often left federal agencies struggling to recover taxpayer funds long after they had vanished into fraudulent accounts. By prioritizing a proactive stance, the government aims to establish a digital and physical perimeter that identifies bad actors at the point of entry. This pivot is expected to secure approximately $90 billion in savings over the next ten years, fundamentally altering the fiscal trajectory of the nation’s primary healthcare safety nets while ensuring that resources remain dedicated to legitimate medical needs.
Economic Incentives and Strategic Shifts
The financial landscape of federal healthcare programs underwent a significant evaluation as the CRUSH rule emerged from recent fiscal successes. During fiscal year 2025, program integrity initiatives achieved a record-breaking $41.9 billion in savings, representing a substantial increase from the $26.3 billion captured in 2024. This performance metric highlighted an exceptional return on investment, with Medicare integrity programs yielding $22.30 for every dollar expended on oversight. Such data provided the necessary political and economic leverage for the administration to propose a more aggressive regulatory environment. The goal shifted from simple recovery to a total preventative overhaul, ensuring that the federal budget remained insulated from the escalating costs of organized healthcare crime. By institutionalizing these high-yield tactics, the government sought to stabilize the long-term solvency of insurance programs that millions of vulnerable Americans rely on for daily care.
Strategic goals under the new framework emphasized a culture of transparency that extended beyond simple accounting practices. CMS designed the CRUSH rule to function as a discretionary, standalone package capable of addressing the most sophisticated forms of waste and abuse. Instead of focusing solely on small-scale billing errors, the regulation targeted the structural vulnerabilities that allowed illicit organizations to exploit program gaps. This required a fundamental realignment of how the government screens providers and audits medical data. By mandating stricter reporting and increasing ownership visibility, the policy created an environment where fraudulent actors faced immediate barriers to entry. The emphasis remained on protecting the fiscal health of the Marketplace and Medicaid while fostering a system that rewarded honest providers. Consequently, the strategic shift aimed to modernize the entire administrative backbone of the Department of Health and Human Services.
Modernizing Oversight Within Medicare Systems
Within the Medicare ecosystem, the CRUSH rule specifically prioritized the elimination of upcoding and diagnostic inflation within Medicare Advantage and Part D plans. These sectors often faced challenges regarding the accuracy of beneficiary risk scores, which directly dictated the level of federal payment. The proposed rule introduced enhanced Risk Adjustment Data Validation audits to ensure that every diagnosis submitted by an organization was substantiated by tangible medical records. This change meant that insurers could no longer rely on vague clinical assertions to justify higher reimbursement rates. Furthermore, the regulation established a mandatory fraud reporting system, requiring private sponsors to notify CMS of any suspicious activity in real time. This immediate communication loop was intended to shorten the detection window for emerging schemes, allowing federal investigators to freeze suspicious payments before they were processed through standard billing cycles.
Beyond financial auditing, the regulation tightened the physical requirements for maintaining a valid enrollment within the Medicare program. CMS sought expanded authority to deny or revoke the credentials of any provider who failed to maintain a verifiable business location or refused to disclose complete ownership information. These physical inspections became a critical component of the vetting process, ensuring that “ghost clinics” could not operate within the federal system. To complement these internal controls, the rule also addressed the rise of predatory marketing aimed at seniors. It prohibited medical supply companies from engaging in unsolicited contact, such as door-to-door visits, unsolicited text messages, or deceptive social media campaigns. By shielding beneficiaries from these intrusive tactics, the government aimed to prevent the initial point of contact for many fraudulent schemes while reinforcing the professional standards expected of all healthcare participants.
Unifying Federal and State Enforcement
One of the most significant hurdles in healthcare fraud prevention was the lack of coordination between various state and federal jurisdictions. The CRUSH rule addressed this fragmentation by harmonizing the enforcement efforts of Medicaid and the Children’s Health Insurance Program across state lines. Under the new guidelines, state authorities gained the ability to determine a “credible allegation of fraud” based directly on findings from federal agencies or other regional jurisdictions. This meant that a provider who faced suspension in one state could no longer simply relocate and resume billing activities in a neighboring region. By creating a unified front, the regulation closed the loopholes that bad actors historically exploited to stay one step ahead of the law. This collaborative synergy ensured that the entire network of taxpayer-funded insurance operated under a single, rigorous standard of integrity, making it far more difficult for repeat offenders to remain active.
To support this unified enforcement, the government moved to implement standardized data tracking through the universal use of National Provider Identifiers for all participants in Medicaid and CHIP. By requiring states to collect and utilize these identifiers, CMS created a centralized database that could track a provider’s history across multiple programs and locations. This level of transparency was matched by stricter enrollment standards that aligned Medicaid denial grounds with those used in Medicare. States were also tasked with providing more robust monthly reports regarding provider terminations and ownership changes, ensuring that the federal government maintained a current and accurate picture of the provider landscape. These measures were designed to strip away the anonymity that often protected fraudulent managers and owners of healthcare entities. By exposing the individuals behind corporate shells, the rule provided a clear path for permanent debarment.
Securing the Health Insurance Marketplace Infrastructure
The Health Insurance Marketplace faced unique challenges related to unauthorized enrollments and the conduct of unscrupulous intermediaries who often manipulated consumer data for illicit gain. The CRUSH rule introduced aggressive accountability measures designed to protect the integrity of the Exchange and the privacy of individual applicants. Under the new provisions, CMS obtained the authority to immediately suspend a broker’s agreement based on a preponderance of evidence indicating abusive conduct. This lower evidentiary standard allowed the government to act swiftly to protect consumers before a full investigation concluded. Furthermore, individuals with specific felony convictions or those who were debarred from other federal programs were barred from participating in the Marketplace entirely. This zero-tolerance policy placed the burden of proof on the brokers themselves, who were required to refute any noncompliance within a thirty-day window or face permanent termination.
In response to the growing threat of international cybercrime, the regulation established strict geographic and technical restrictions on how agents and brokers access Marketplace systems. The rule specifically banned the use of Virtual Private Networks to mask foreign locations, requiring all traffic to originate from within the United States. This measure was a direct response to international fraud rings that attempted to compromise the digital infrastructure of the American healthcare system from abroad. By implementing these technological barriers, the government sought to ensure that only legitimate, domestic professionals could interact with sensitive consumer information. These safeguards were paired with requirements for brokers to implement more robust internal security protocols, further hardening the Marketplace against external attacks. This comprehensive approach to digital security recognized that modern healthcare fraud often occurs in the digital realm, requiring sophisticated technical solutions to maintain public trust.
Moving Toward a New Standard of Accountability
The implementation process for these regulations involved a collaborative period where stakeholders and the general public were invited to shape the final technical nuances of the policy. CMS established a public comment period that extended into early 2027, ensuring that healthcare providers and insurance organizations had a platform to voice their concerns. This phase allowed for a balanced dialogue between the necessity of rigorous enforcement and the operational realities of managing large-scale medical systems. By engaging with the industry, the government aimed to refine the rules to avoid placing undue burdens on legitimate providers while maintaining the strength of the fraud prevention measures. This transparent approach was viewed as essential for building a sustainable framework that could adapt to the evolving tactics of fraudulent organizations. The dialogue underscored a shared commitment to maintaining a fair and honest system for all American taxpayers and patients.
Ultimately, the CRUSH rule functioned as a catalyst for a more resilient and transparent healthcare infrastructure that prioritized long-term fiscal solvency. The government succeeded in shifting the focus from reactive recovery to proactive prevention, establishing a new standard for how federal programs protected their assets. Actionable steps for healthcare organizations included the immediate audit of internal enrollment data and the strengthening of cybersecurity protocols to meet the new domestic access requirements. Providers were encouraged to implement more rigorous internal compliance programs to ensure that all diagnostic data remained fully substantiated by medical records. By addressing the root causes of systemic waste and abuse, the regulation paved the way for a more secure future for Medicare and Medicaid. These efforts ensured that every taxpayer dollar was directed toward its intended purpose, fostering a system that was both accountable to the public and protective of the most vulnerable.