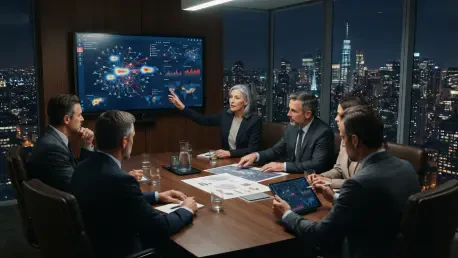
The rapid escalation of digital threats has forced a fundamental reconfiguration of corporate power structures, moving cybersecurity from the server room directly to the boardroom mahogany. In the current landscape, organizations recognize that cyber resilience is no longer a technical luxury but a fundamental pillar of enterprise risk management. Industry research indicates that while reporting frequency and formal integration have reached record highs, a troubling paradox has emerged: the more information directors receive, the less confident they feel in managing the risk. This analysis examines how boards govern these invisible threats when data volume often outpaces strategic comprehension.
The Transition of Cybersecurity to the Boardroom Floor
In the modern corporate landscape, cybersecurity has undergone a radical transformation, migrating from the isolated confines of IT departments to the center of boardroom agendas. As digital threats become more sophisticated and impactful, organizations are recognizing that resilience is essential for survival. This shift explores findings that examine how boards attempt to govern these pervasive threats. While the frequency of reporting has reached record levels, a significant gap remains. The more information directors receive, the less confident many feel in their ability to truly manage the risk effectively.
Evolution of Governance and the Rise of Financial Accountability
Historically, boards viewed cybersecurity as an operational nuisance, often delegating it entirely to technical officers. However, high-profile data breaches and the subsequent collapse of shareholder value shifted the paradigm toward accountability. Approximately 70% of organizations now formally weave cyber risk into their enterprise-level frameworks. This historical shift is marked by a transition from qualitative scenarios to quantitative financial modeling. Today, 60% of organizations attempt to put a dollar value on potential cyber losses, reflecting a trend where cyber risk is treated with the same fiscal rigor as market volatility.
Navigating the Disconnect Between Data and Understanding
Navigating the complexities of modern governance requires a bridge between technical execution and strategic oversight. Despite the fact that 65% of boards receive quarterly updates on the threat landscape, a deep-seated confidence gap persists among leadership. Only 55% of directors report feeling truly well-informed about the specific threats targeting their firms. This suggests a breakdown in communication; while the volume of data being shared is high, its utility is often low. Boards are frequently inundated with technical jargon that does not translate into strategic insight.
The Persistence of the Boardroom Confidence Gap
Technical teams often concentrate on the mechanics of an attack, while directors require a focus on the resulting impact on business continuity. This discrepancy often leaves leadership in a state of perpetual catch-up, reacting to headlines rather than anticipating vulnerabilities. When information is presented without business context, it fails to trigger the necessary risk-mitigation behaviors. Consequently, the disconnect between reporting frequency and actual understanding remains a major hurdle to achieving a state of proactive defense in a volatile market.
The Mystery of Security ROI and Risk Reduction
A striking revelation in current patterns is that only 46% of respondents believe their board understands how security spending actually reduces risk. This disconnect highlights a failure in translating security efficacy into business terms. If a board cannot see the direct correlation between a multi-million dollar investment and a measurable decrease in the likelihood of a breach, they are effectively flying blind. This lack of clarity complicates the decision-making process, often leading to reactive spending after an incident occurs rather than proactive investment based on a calculated return.
Third-Party Vulnerabilities and the AI Threat Vector
Emerging risks that transcend traditional corporate perimeters are adding to the complexity of the digital landscape. While phishing and ransomware remain primary concerns, anxiety regarding third-party software vulnerabilities and the misuse of Artificial Intelligence is rising sharply. Global supply chains mean that a vulnerability in a minor vendor can provide a backdoor into a massive corporation. Furthermore, the advent of generative AI has equipped bad actors with tools to automate attacks at scale. Addressing these complexities requires boards to look beyond their own firewalls and consider the health of their entire digital ecosystem.
Market Projections: The Future of Resilience and Regulatory Pressure
The trajectory of cyber risk oversight will be defined by increased personal accountability for directors. Regulators are looking at whether boards have exercised due care in their oversight of digital assets. From 2026 to 2028, a shift toward standardized disclosure requirements is expected. Technologically, standalone cyber insurance will continue to grow, as combined policies often prove insufficient for specialized costs like forensics. As the market matures, insurers may effectively become secondary regulators, dictating the security standards required for corporate hygiene.
Strategic Frameworks for Bridging the Oversight Gap
To close the confidence gap, boards must move beyond passive reporting and adopt an inquisitive, hands-on approach to risk. Organizations should prioritize risk quantification to make data actionable for non-technical directors. Companies should invest in standalone cyber insurance policies, which provide financial protection and access to breach response specialists. Finally, incident response plans must be regularly tested through tabletop exercises involving the board. By simulating a crisis, directors can identify gaps in their understanding and decision-making processes before a real-world disaster strikes.
Securing the Future Through Informed Governance
The transition of cybersecurity into the board mandate represented a necessary response to a volatile environment. Analysis revealed that moving beyond awareness required a cultural shift where leadership teams moved past static reports toward active participation in cyber-readiness. It was clear that the most effective strategies integrated cyber insurance directly into security budgets to catalyze hygiene. By focusing on financial materiality, boards finally aligned digital security with organizational goals. This historical alignment proved that the confidence gap was a bridge built through business-aligned communication.